Understanding PHP2Shell: What It Means for Your WordPress Site
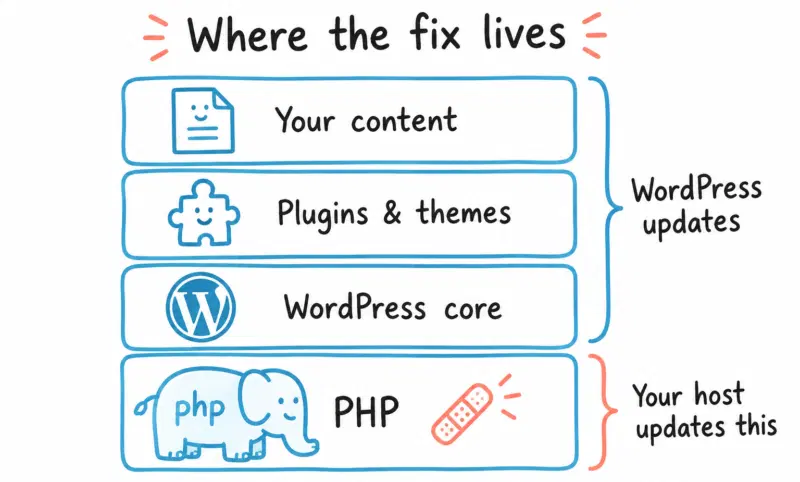
You might have heard recent tech news about PHP2Shell—a critical security flaw affecting PHP, the programming language that runs WordPress behind the scenes.
Because PHP lives beneath WordPress on your server rather than inside it, standard WordPress updates or security plugins cannot fix it on their own. It requires a direct server-level update to PHP.
What This Means for 35sites Clients
If your website is hosted and managed with 35sites, you are completely covered.
We monitor server infrastructure closely and have already applied the necessary updates and patches to ensure your environment is secure against PHP2Shell. You do not need to take any action or change anything on your site.
What If You Host Elsewhere?
If you host your WordPress site on a different platform or server provider, you will need to verify your status directly with them:
- Check with Your Host: Contact your hosting provider’s support team and ask if the server-level PHP fix for PHP2Shell has been fully installed.
- Watch for Updates: If you maintain external hosting environments, keep an eye out for direct instructions or alerts regarding your server configurations.
If you have any questions about your hosting setup or need guidance on keeping your sites secure, feel free to reach out!
P.S 🛠️ For the Tech Folk: How PHP2Shell Affects Systems
- The Core Vulnerability: PHP2Shell consists of two high-severity flaws (CVE-2026-109618 and CVE-2026-109619, both rated 9.2/10) discovered in PHP.
- The Attack Vector: They allow an unauthenticated remote attacker to send a specially crafted request directly to a server, bypassing application-layer checks and executing arbitrary code. Because the execution happens at the PHP engine layer before WordPress initializes, standard WAF rules, security plugins, or maintenance modes are completely bypassed.
- The Fix & Version Target: Requires patching PHP binaries to the latest patched releases (8.5.12, 8.4.27, 8.3.36, or 8.2.35). While sites can be secured on supported branches, the goal is for everyone to run PHP 8.4 or 8.5, with PHP 8.3 acting as the absolute minimum floor for a secure environment. Older, end-of-life versions (8.1 and below) lack official security updates and leave environments exposed unless explicitly backported by vendors.